From Splunk to Sigma: Building and Validating Vendor-Neutral Detection Logic
A detection-engineering exercise using Sigma, Splunk, Windows telemetry, and Atomic Red Team to validate vendor-neutral detection logic
A detection-engineering exercise using Sigma, Splunk, Windows telemetry, and Atomic Red Team to validate vendor-neutral detection logic
How to Validate PowerShell Detections in Splunk with Sysmon, Atomic Red Team, and MITRE ATT&CK
Exploring the new skills, technologies and investigative mindset behind TryHackMe's updated L2 curriculum
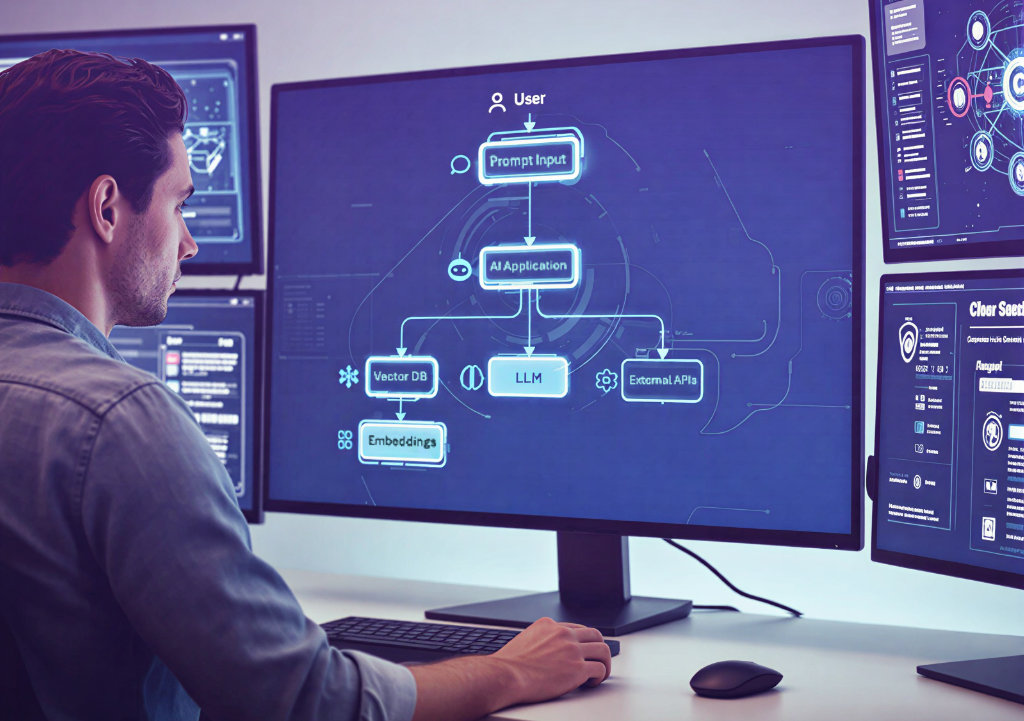
My Experience with INE’s AI Systems Security Specialist (eAIS) Learning Path
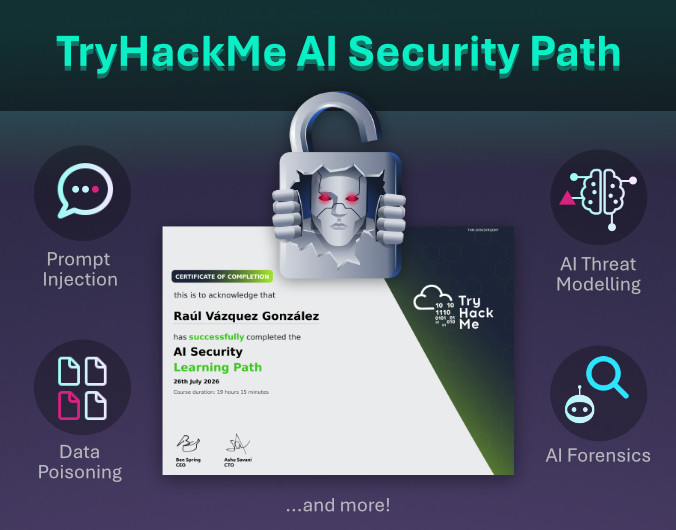
A reflection on completing TryHackMe’s AI Security learning path
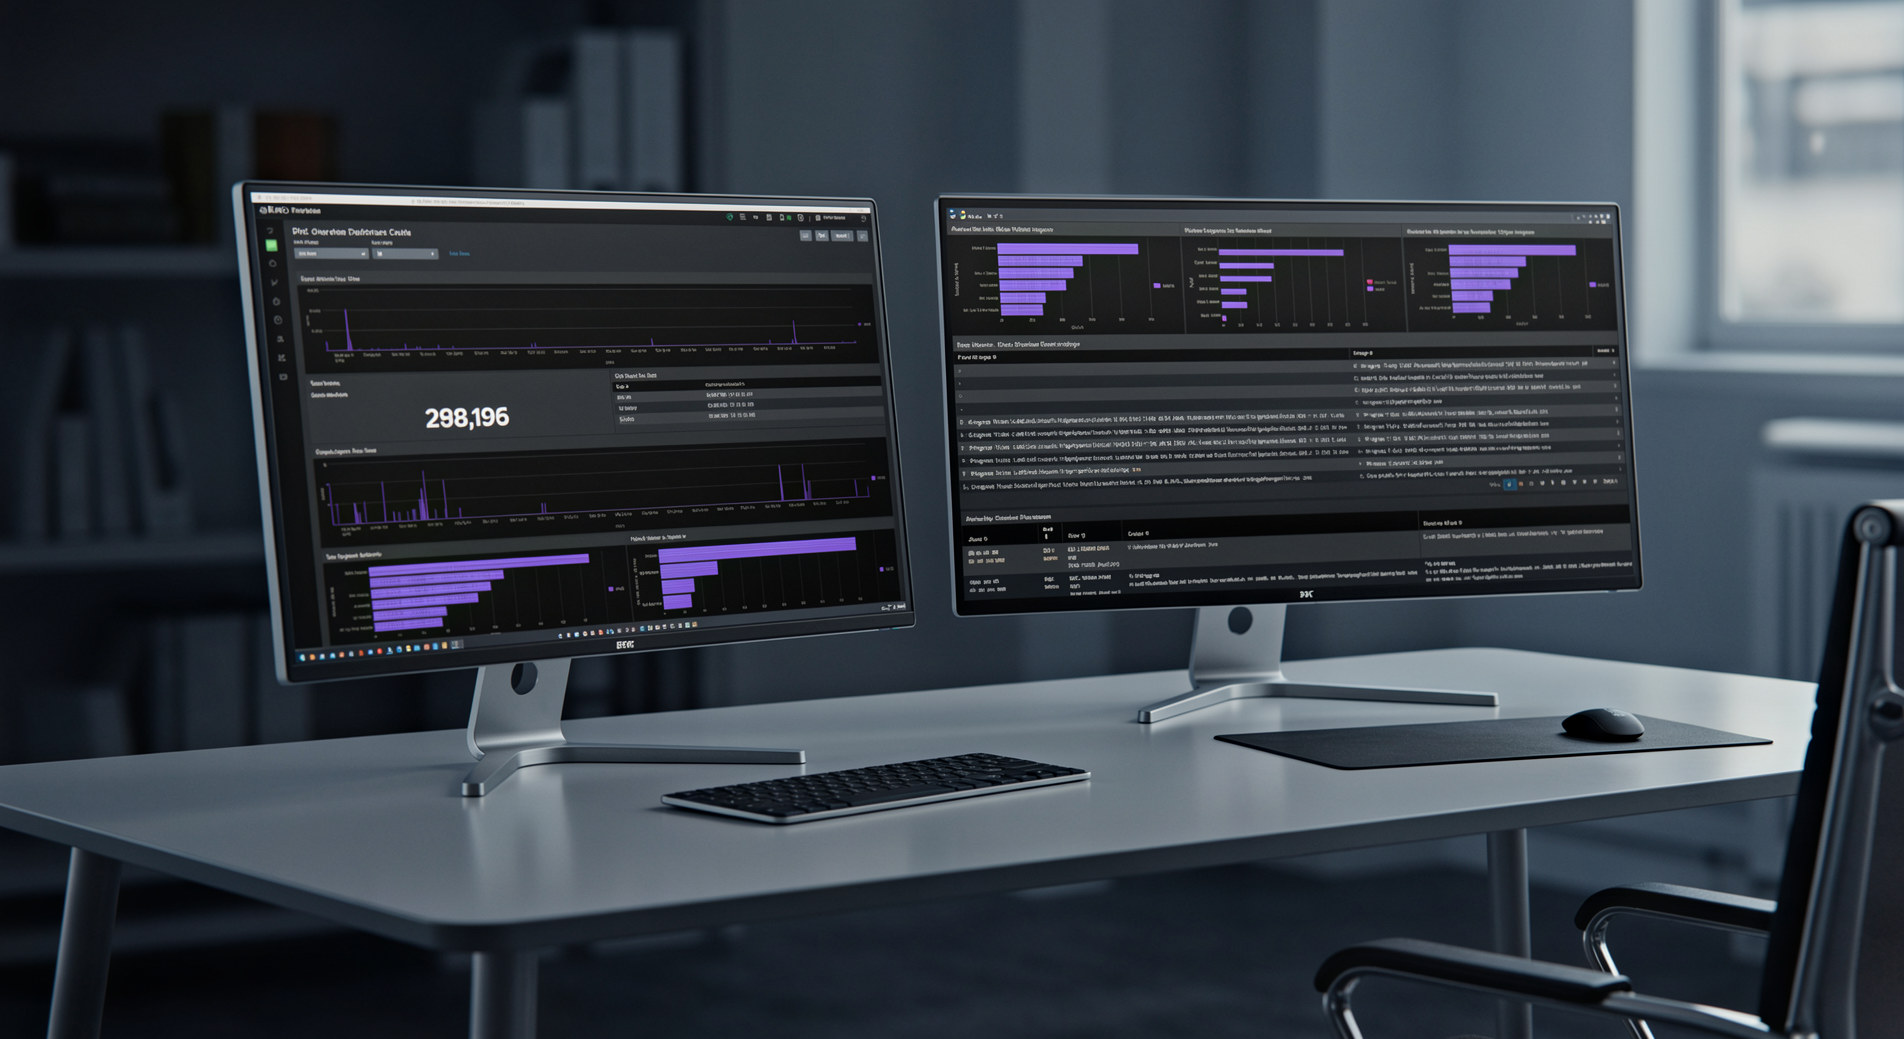
Designing an Operational Monitoring Dashboard for Authentication, Endpoint, Network, and Threat Hunting Visibility
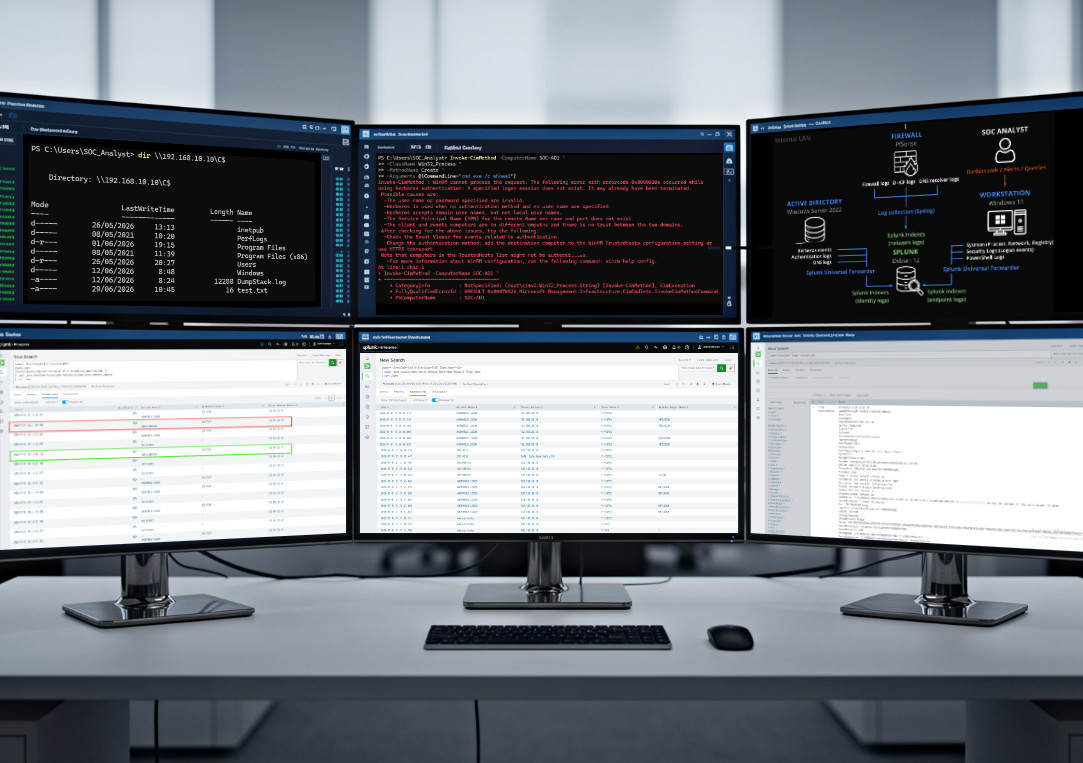
Correlating failed logons, Kerberos authentication events, SMB access, and blocked lateral movement attempts in a hardened Active Directory environment
Simulating common PowerShell abuse techniques and investigating endpoint telemetry in Splunk
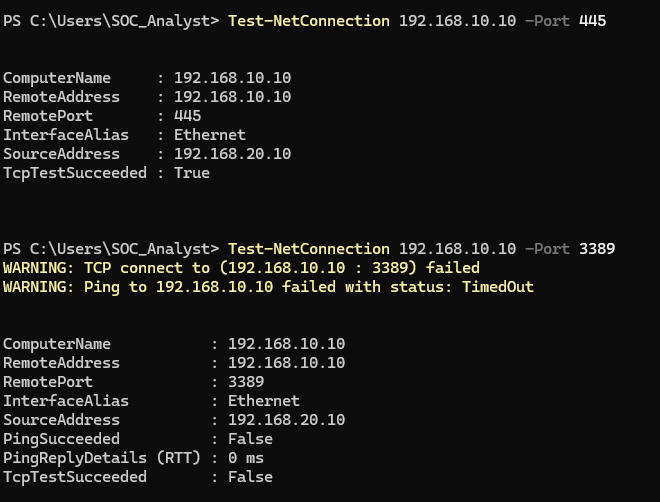
Root Cause Analysis, Fixes and Lessons Learned During My SOC Homelab Deployment
A Complete Write-Up Demonstrating Real SOC Investigation Methodology
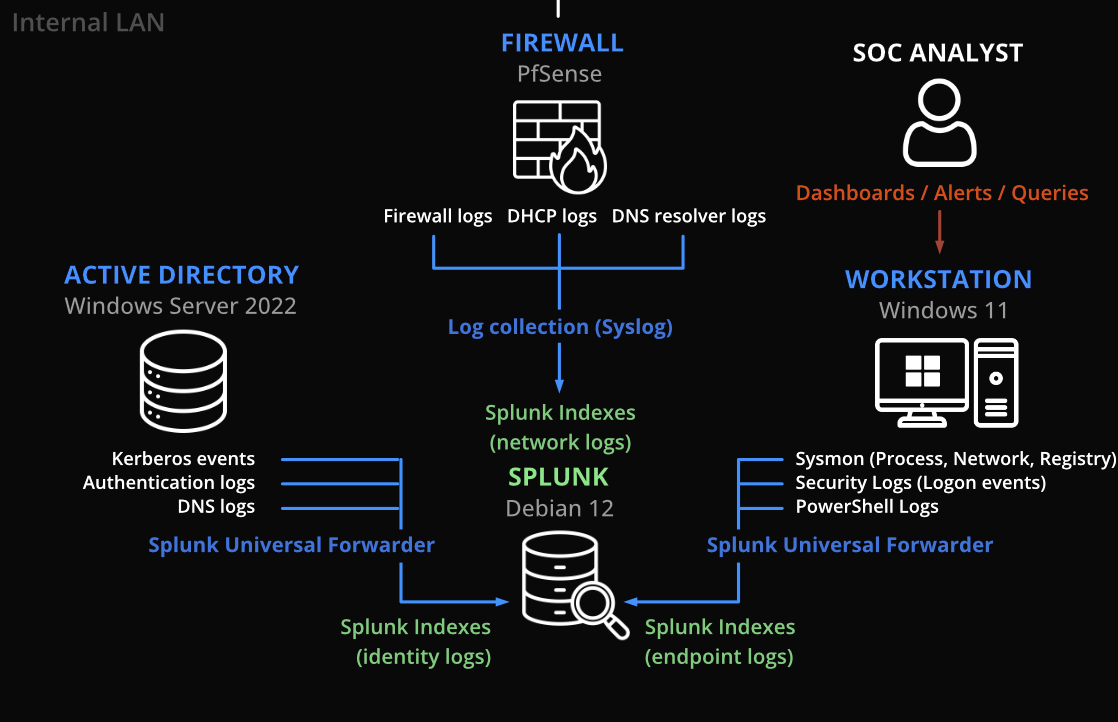
Designing an Enterprise-Style Security Monitoring Environment for Blue Team Skill Development
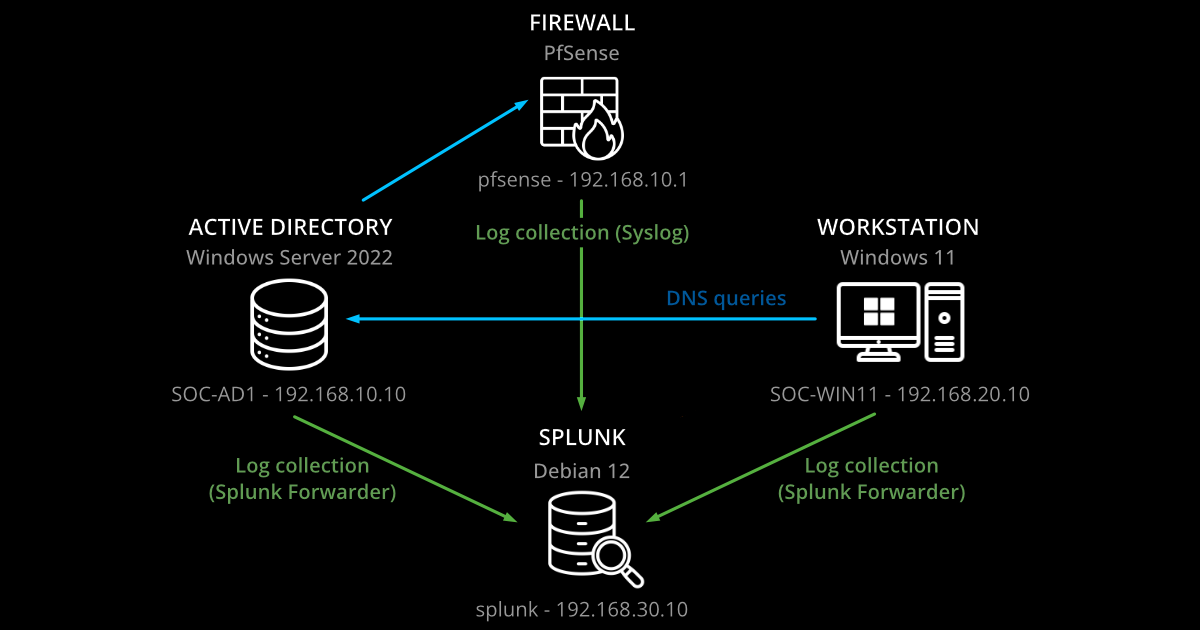
Lessons learned building a SOC homelab with Splunk, Active Directory, Sysmon, and pfSense
A hands-on path into modern blue team operations
Simulating Real-World SOC Triage, Threat Hunting, and Incident Reporting Through a Conti Ransomware Investigation
A hands-on DFIR walkthrough covering phishing analysis, malicious macros, memory forensics, C2 investigation, and persistence detection.
Hands-on Splunk investigation covering ransomware deployment, persistence mechanisms, lateral movement, and AWS data exfiltration
Network Traffic Analysis and Forensics to Identify C2 Channels, ARP Spoofing, and Data Exfiltration Techniques
A SOC Threat Intelligence Investigation into Brute Force, File Upload Exploitation, and Web Shell Persistence
Context is the key to understanding modern cyber threats
A SOC Threat Intelligence Investigation into Brute Force, File Upload Exploitation, and Web Shell Persistence
A SOC phishing analysis; email header forensics, obfuscated payload decoding, and adversary attribution
A practical walkthrough of SOC investigation techniques, including IOC analysis, malware classification, and MITRE ATT\&CK mapping
Practical Log Analysis from the Boss of the SOC (BOTS v2) Dataset
Practical Log Analysis from the Boss of the SOC (BOTS v2) Dataset
A practical SOC-style investigation walkthrough using Windows telemetry to identify attacker activity and defense evasion techniques.
A practical SOC analyst investigation of malicious hashes, phishing techniques, and malware delivery chains from the Invite Only TryHackMe room
A Complete Guide to Solving TryHackMe’s Wireshark Traffic Analysis Room - A Step-by-Step Walkthrough of All Tasks and Insights
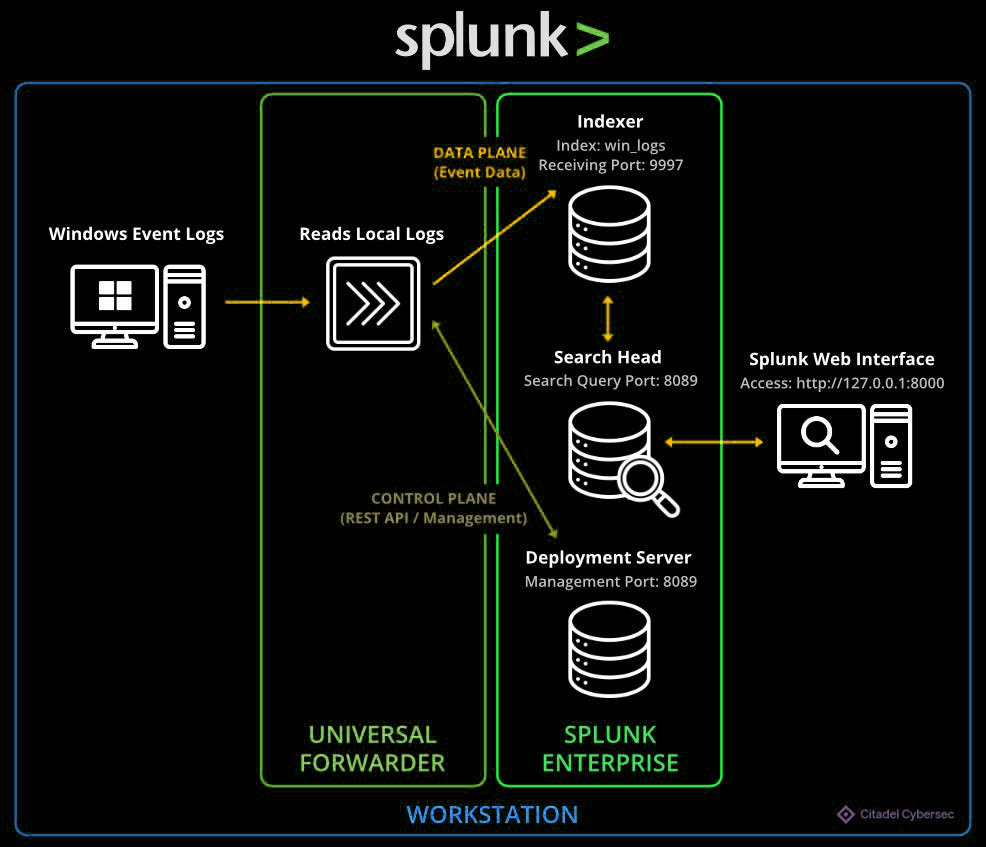
A step-by-step hands-on lab to practice Windows log ingestion, SPL commands, reporting and dashboard creation using Splunk Enterprise
A TryHackMe Regex Practical Exercise Writeup
Essential ELK techniques for investigating and querying logs
Identifying cleartext credentials inside packet captures and generating actionable firewall rules
Complete writeup with binary analysis, string decoding, and DFIR techniques
A breakdown of the SAL1 exam, its SOC scenarios, tools, and how to prepare effectively using TryHackMe
A TryHackMe writeup from the “Detecting Web Shells” room — Task 6 Investigation
Unlocking Encrypted Traffic - From TLS Handshake to Decrypted HTTP/2 Data
TryHackMe Sysmon Task 10 - Practical Investigations Explained (With PowerShell)
Anomalous user agents, subtle anomalies in packet data and specific attack patterns
TryHackMe Detecting Web DDoS Room, Task 5 Writeup
ICMP and DNS exfiltration techniques and malicious cleartext FTP behavior
Practical examples of how to use Wireshark to answer specific questions about network activity
TryHackMe — Network Security Essentials (Task 7 Practical Exercise)
Using Brim capabilities to identify malicious activities
Analyzing network traffic to identify ARP requests, HTTP packets, and sniffed login credentials
Solving Rotten Cloud Investigation — Blue Team Labs Online (Halloween 2025 Special Event)
Investigating a .pcap file to analyze a suspected Nmap scan
TryHackMe Snapped Phish-ing Line Room Write‑Up
Investigating PCAP files and email metadata
Now getting ready for the job got even better
Learn how to detect and block brute-force and reverse shell attacks using Snort IDS/IPS
Using Eric Zimmerman’s Registry Explorer to locate key forensic artifacts
Fine-tune Snort rules for effective packet analysis
A hands-on walkthrough covering Snort IDS rule creation, traffic analysis, signature-based detection and troubleshooting
A Broad and Professional Blue-Team Skillset
A detailed writeup of TryHackMe’s “Investigating with Splunk” final question
Practical experience with the Google Cybersecurity Certificate
Master UFW and Kernel Hardening to Fortify Your Linux Workstation Against Threats
Practical experience with the Google Cybersecurity Certificate
Identifying Tactics, Techniques and Procedures of an APT
Practical experience with the Google Cybersecurity Certificate
All the Ways to Disable Bluetooth for Good
Practical experience with the Google Cybersecurity Certificate
Excellent cybersecurity fundamentals with practical assignments
